MDSAP Issues REPs User Access Request Form
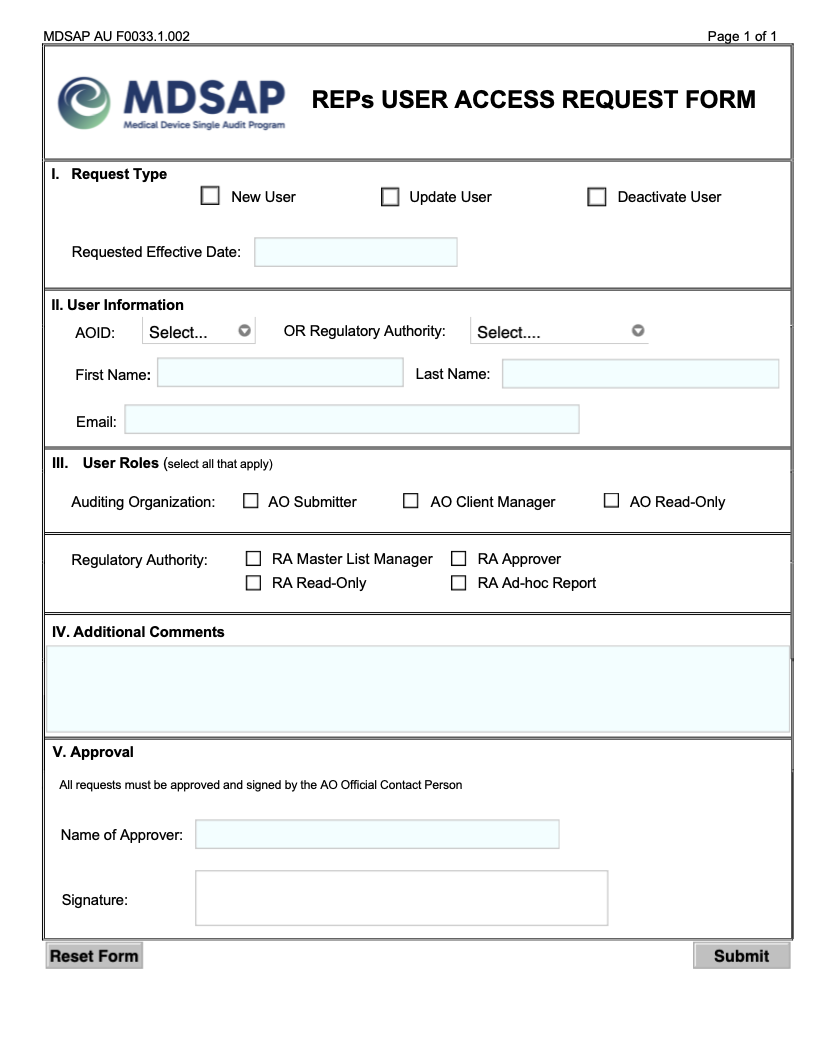
The Medical Device Single Audit Program, MDSAP, has issued the REPs User Access Request Form, identified as MDSAP AU F0033.1.002.
The form is designed to manage user access requests within REPs, including requests to create, update or deactivate users.
Request Types
The form provides three request options:
New User
Update User
Deactivate User
It also includes a field for the requested effective date.
User Information
The form requires information identifying the user and associated organisation or authority.
This includes:
AOID or Regulatory Authority;
first name;
last name;
email address.
Auditing Organization Roles
For users associated with an Auditing Organization (AO), the form allows selection of the following roles:
AO Submitter
AO Client Manager
AO Read-Only
These role options allow access to be assigned according to the user’s responsibilities within the organisation.
Regulatory Authority Roles
For users associated with a Regulatory Authority (RA), available roles include:
RA Master List Manager
RA Approver
RA Read-Only
RA Ad-hoc Report.
The form allows multiple roles to be selected where appropriate.
Additional Comments
A dedicated section is provided for additional comments, allowing relevant information or context to be included with the access request.
Approval Requirement
The form includes a formal approval section.
All requests must be approved and signed by the AO Official Contact Person. The form therefore requires the name of the approver and a signature.
Impact on MDSAP Auditing Organizations and Regulatory Authorities
For MDSAP Auditing Organizations, Regulatory Authorities and programme administrators, the form provides a standardised method for managing REPs user access.
Stakeholders should pay particular attention to:
correct request type;
accurate user identification;
selection of appropriate AO or RA roles;
requested effective date;
approval by the AO Official Contact Person;
timely deactivation of users who no longer require access;
internal access governance and role management.
The key message is that REPs access should be managed through a controlled and documented process, with clear user roles and formal approval.